Web app pentesting
Agents attack your apps and APIs like an operator, and prove every finding with a working exploit.
EXPLOREConnect a repository, a cloud account or a URL. Findings from all three land in one dashboard, each with the proof behind it.
Trident pentests your apps and APIs, reviews every pull request and maps attack paths across AWS, Azure, GCP and Kubernetes, then proves what it found.
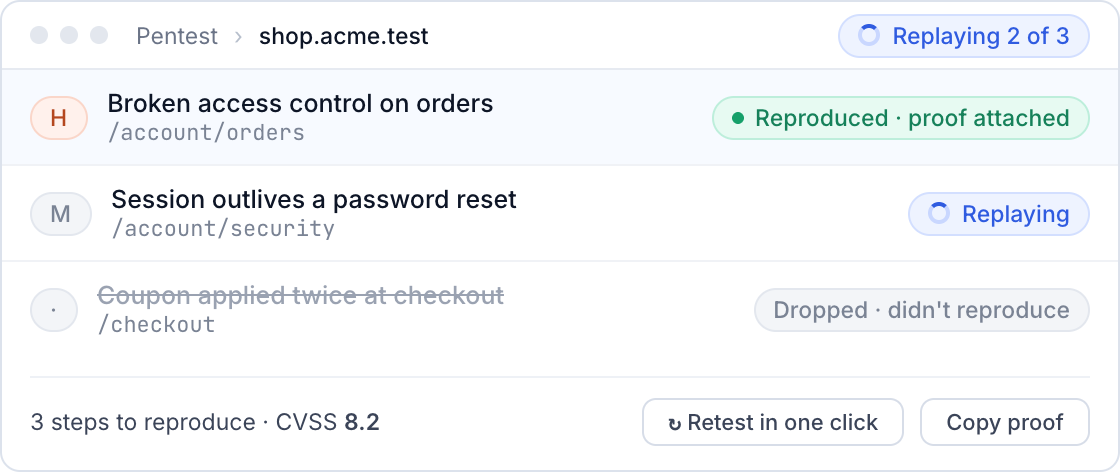
Agents map the app, try each idea and replay every candidate from a clean session. Only what reproduces becomes a finding.
trident-sentinel flags the exact lines on every push, with a fix to commit, and can hold the merge until it is fixed.
Read-only, in minutes. Trident maps everything it can reach across your accounts, ranked by the paths an attacker would take.
Your coding agent pulls a finding over MCP, proof of concept included, and patches it where you already write code.
Every candidate is replayed from a clean session before it counts.What doesn't reproduce is dropped, not reported.Every pentest finding ships with its proof of concept.
Validated by doingRetest in one click after a fixSee a sample finding →
1 of 6 candidates reproduced
Each product has its own page. Connect a repository, a cloud account or a URL, and every finding lands in the same dashboard with its proof.
Agents attack your apps and APIs like an operator, and prove every finding with a working exploit.
EXPLORE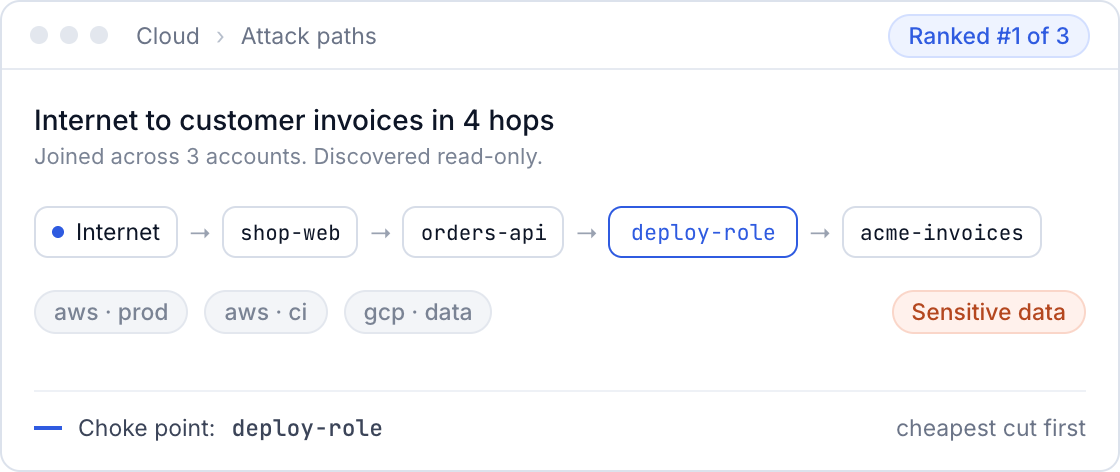
Your cloud as one graph, ranked by what an attacker can actually reach, not by CVSS score.
EXPLORE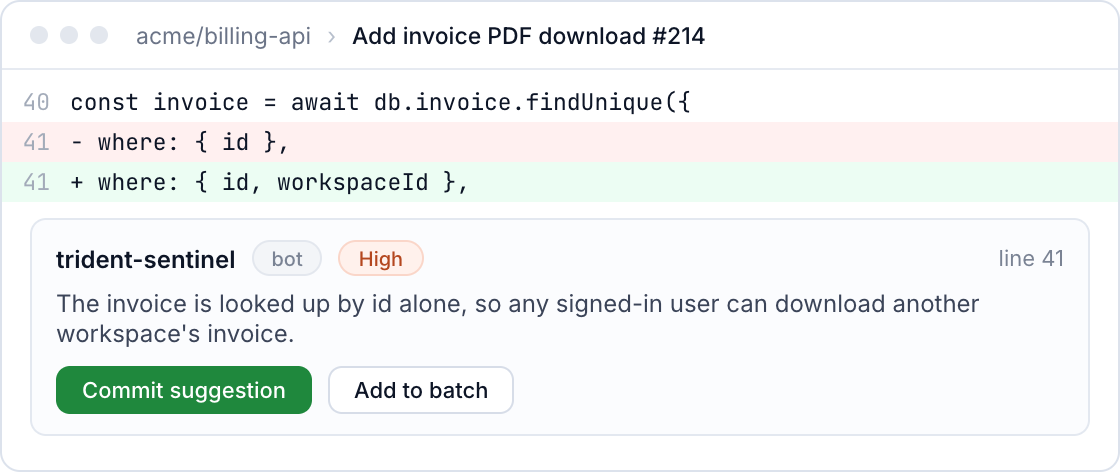
trident-sentinel reviews every pull request and comments on the exact line, with the fix ready to commit.
EXPLORE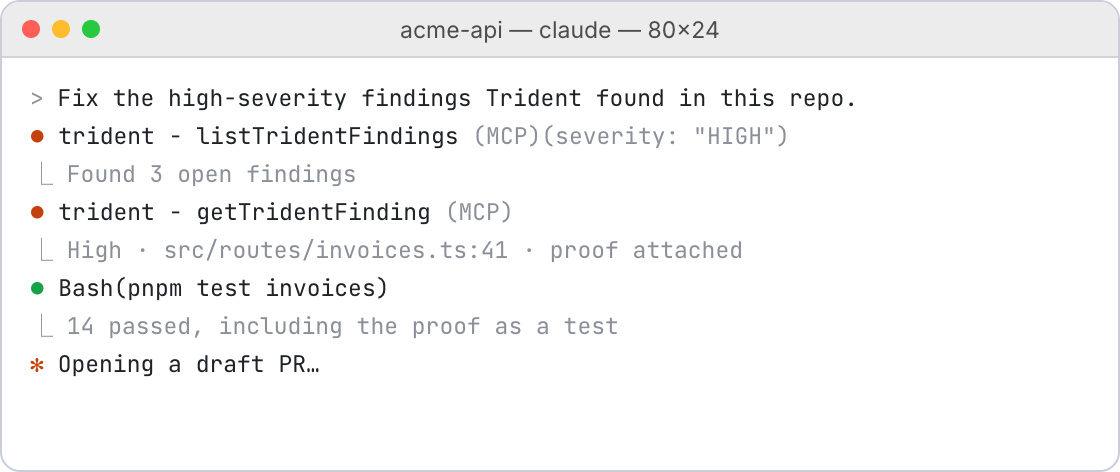
Your coding agent pulls a finding over MCP, proof of concept included. Ask @Trident in Slack and it answers from live findings.
EXPLOREStart a free trial. Your first verified findings land within a day of connecting.